
About STACKTITAN
Security controls are easy to buy. Confidence is much harder to earn.
STACKTITAN was founded on a simple belief: organizations should understand how their defenses perform under real-world adversarial pressure. Not just whether controls have been implemented.
STACKTITAN promotes a Defensive by OffensiveTM cybersecurity methodology and delivers expert-led cybersecurity assessments and advisory programs for organizations that need to understand how their defenses perform under real-world pressure. With red team thinking, purple team collaboration, and platform-assisted delivery, we bring adversarial insight and practical guidance together to help organizations harden and deepen their defenses. Our approach is designed not only to identify vulnerabilities and areas of exposure, but also to provide practical, actionable remediation strategies aligned with institutional risk management objectives, compliance expectations, and cybersecurity best practices.
Unlike traditional security consultancies, STACKTITAN was built by practitioners. Researchers. Developers. Adversarial operators. Security architects. People who have spent their careers understanding how attackers think, how systems fail, and how organizations can better defend themselves.
Our mission is straightforward:
Help organizations move from reactive assessments to continuous attack resilience.
STACKTITAN IN NUMBERS
2
1
2
3
4
5
6
7
8
9
0
1
2
3
4
5
6
7
8
0
YEARS
spanning enterprise, government, critical infrastructure, healthcare, manufacturing, and technology environments.
0
6
2
3
4
5
6
7
8
6
0
1
2
3
0
5
6
7
8
9
0
0
2
3
4
5
6
7
8
0
across applications, cloud environments, networks, connected devices, and enterprise infrastructure.
0
1
2
3
4
5
6
7
8
6
0
1
2
3
4
5
6
7
8
9
%
in attack-path risk through targeted remediation and security improvement initiatives.
0
1
2
3
4
5
6
7
8
1
2
1
2
3
4
5
6
7
2
9
0
1
2
3
4
5
6
7
8
0
+
to test organizational defenses against realistic threat activity.
Industry recognized leadership
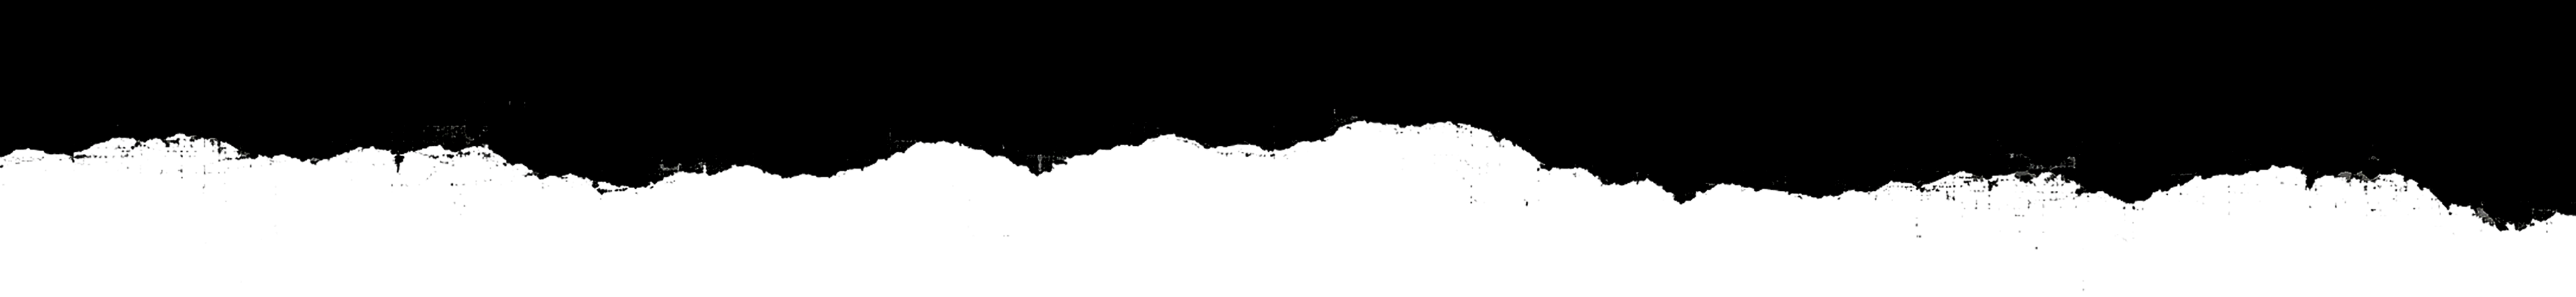
STACKTITAN’s leadership team literally wrote the book on offensive security, co-authoring Black Hat Go, an industry-recognized guide trusted by cybersecurity professionals worldwide.


Team StackTitan
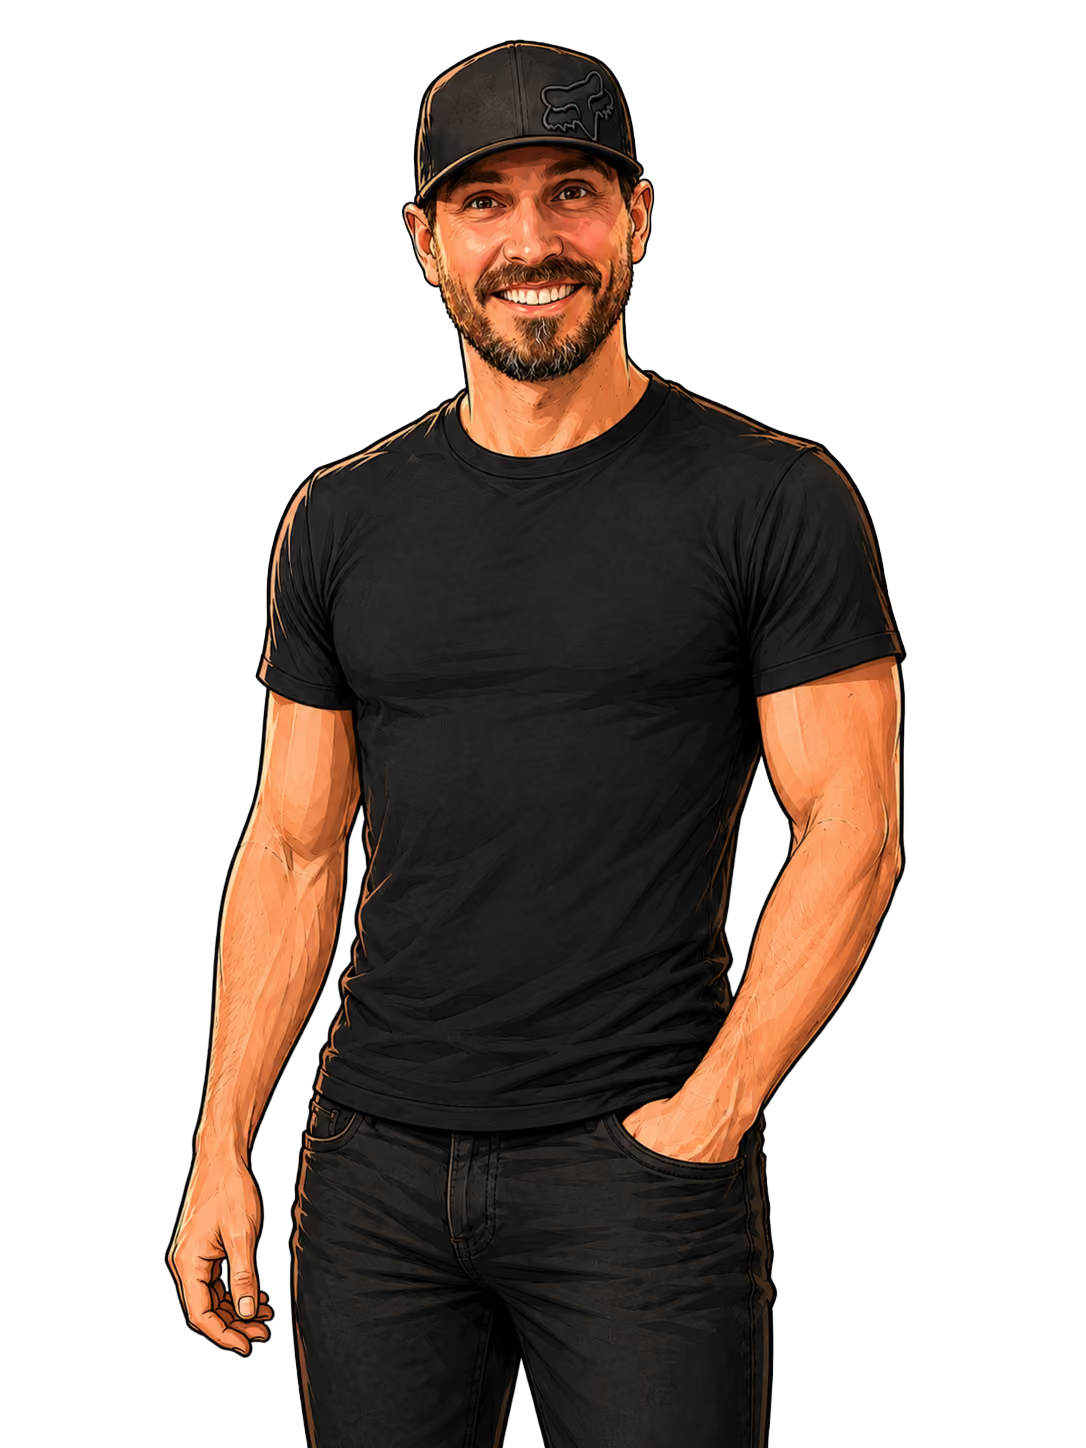
Chris Patten
Co-founder of STACKTITAN and U.S. Air Force veteran with 25+ years of experience spanning military intelligence, enterprise architecture, adversarial simulation, and penetration testing. Published author, researcher, and developer focused on helping organizations understand and defend against modern threats.
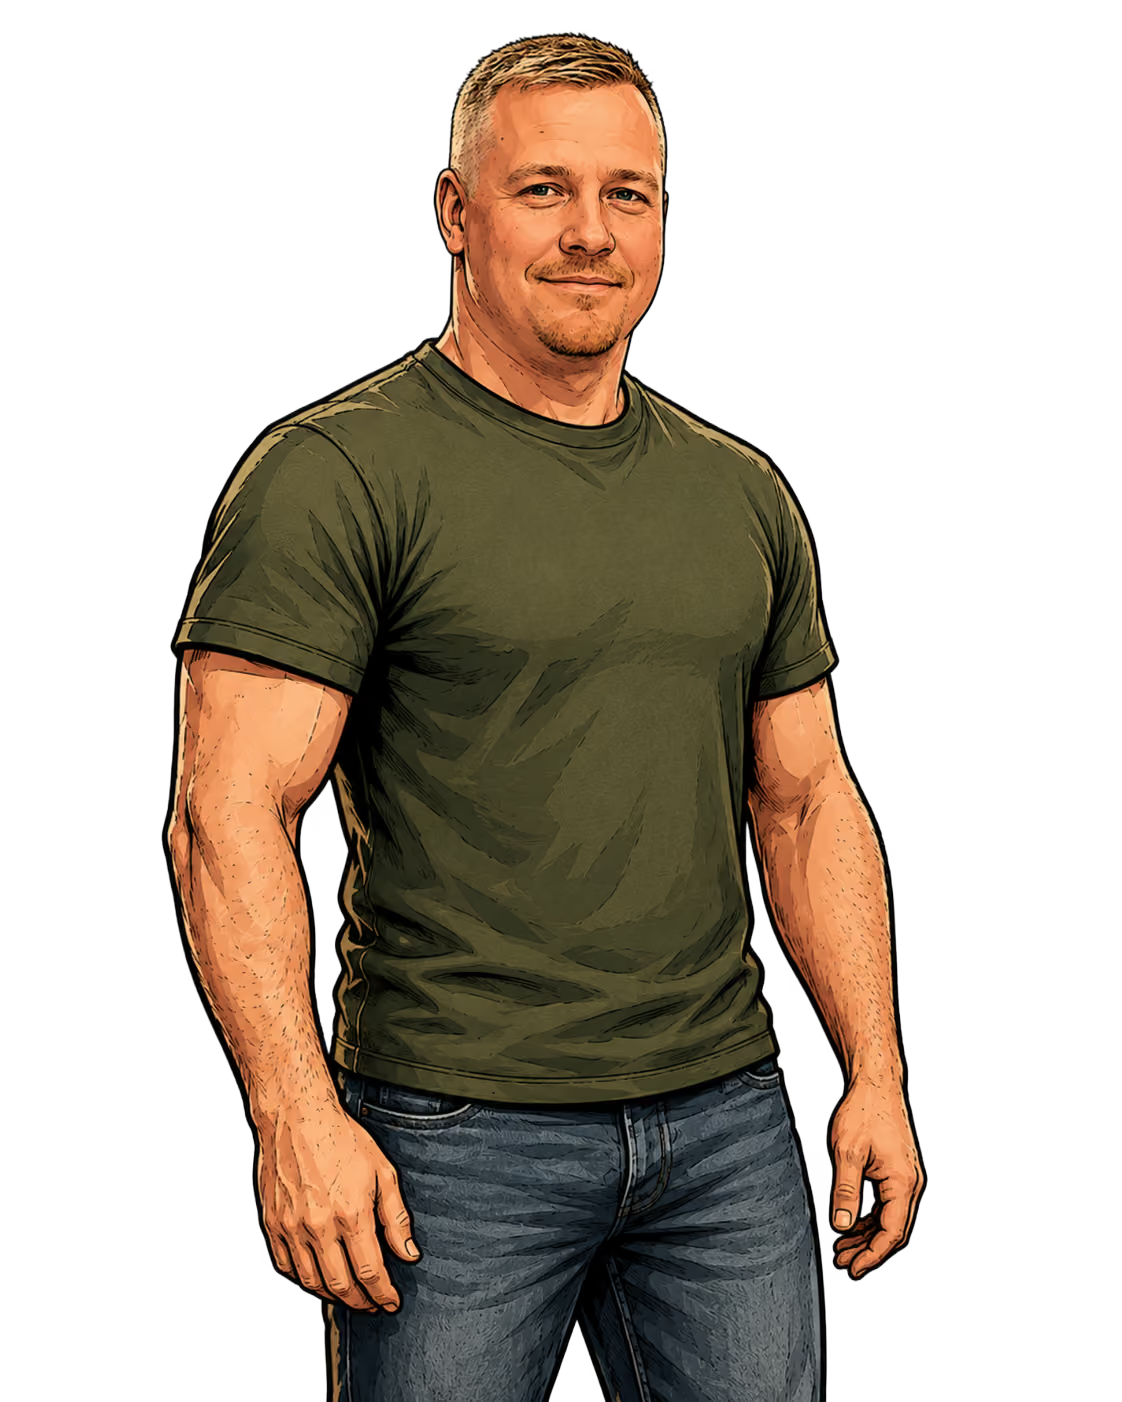
Randy Waterman
U.S. Army veteran with extensive experience in cybersecurity strategy, risk management, and solution architecture. Randy helps organizations align security programs with business objectives, reduce risk, strengthen resilience, and support long-term growth.
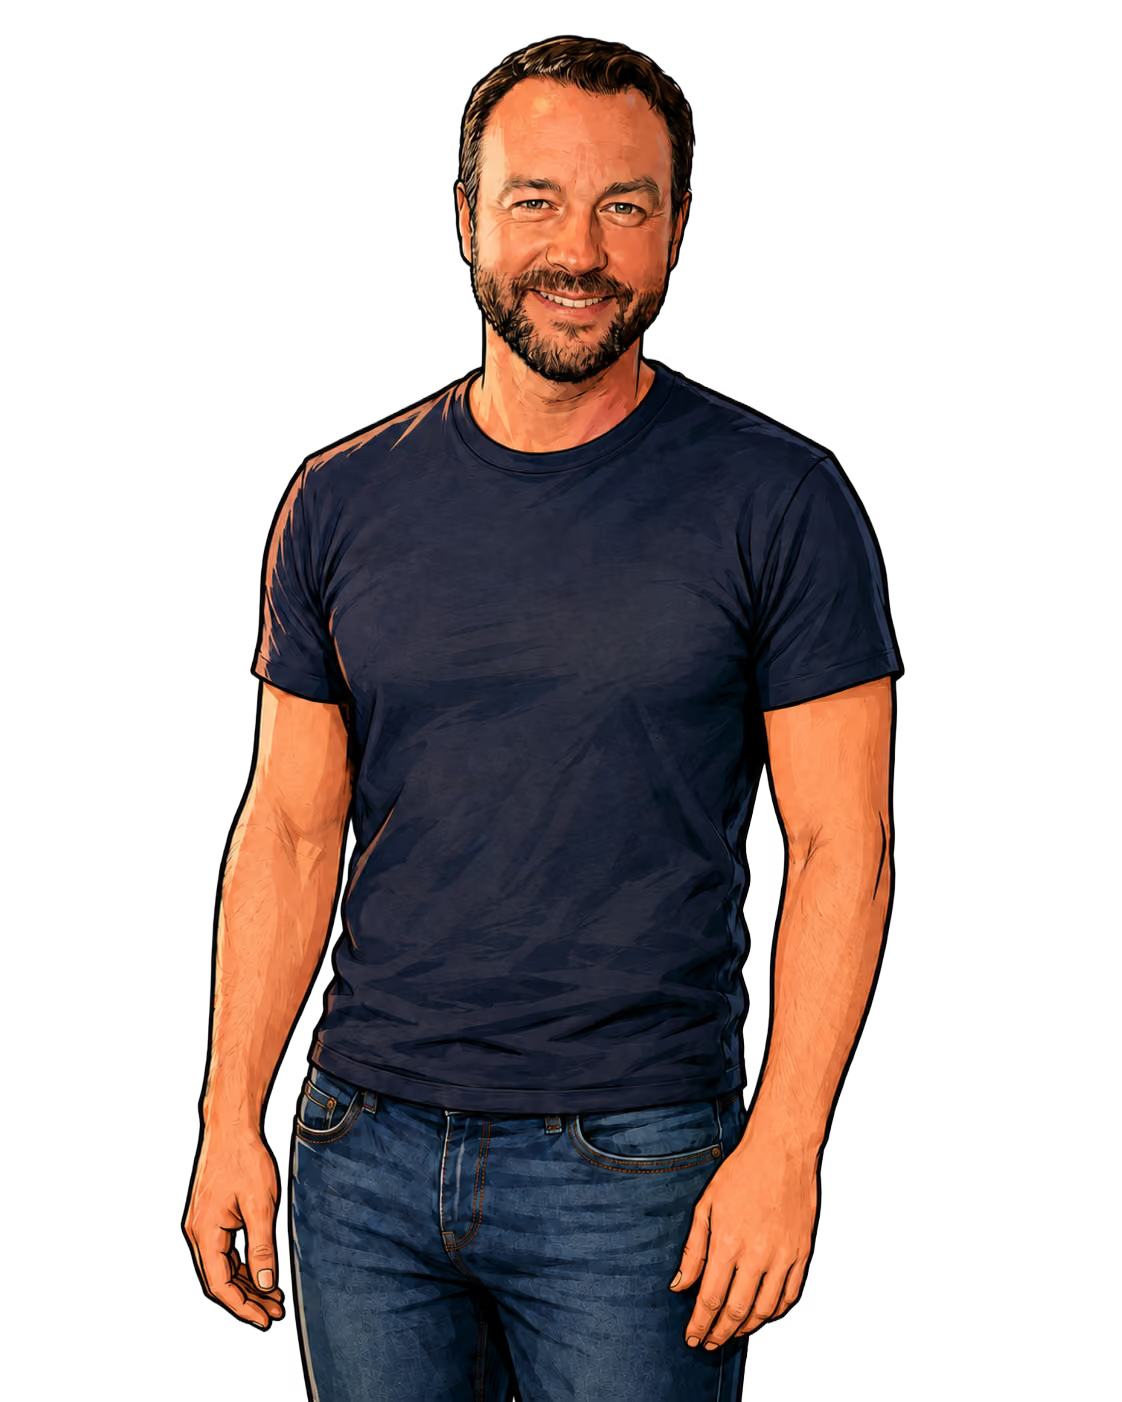
Dan Kottmann
Co-founder of STACKTITAN and researcher specializing in application security, penetration testing, social engineering, and adversarial simulation. Co-author of Black Hat Go and contributor to numerous offensive security tools and methodologies.
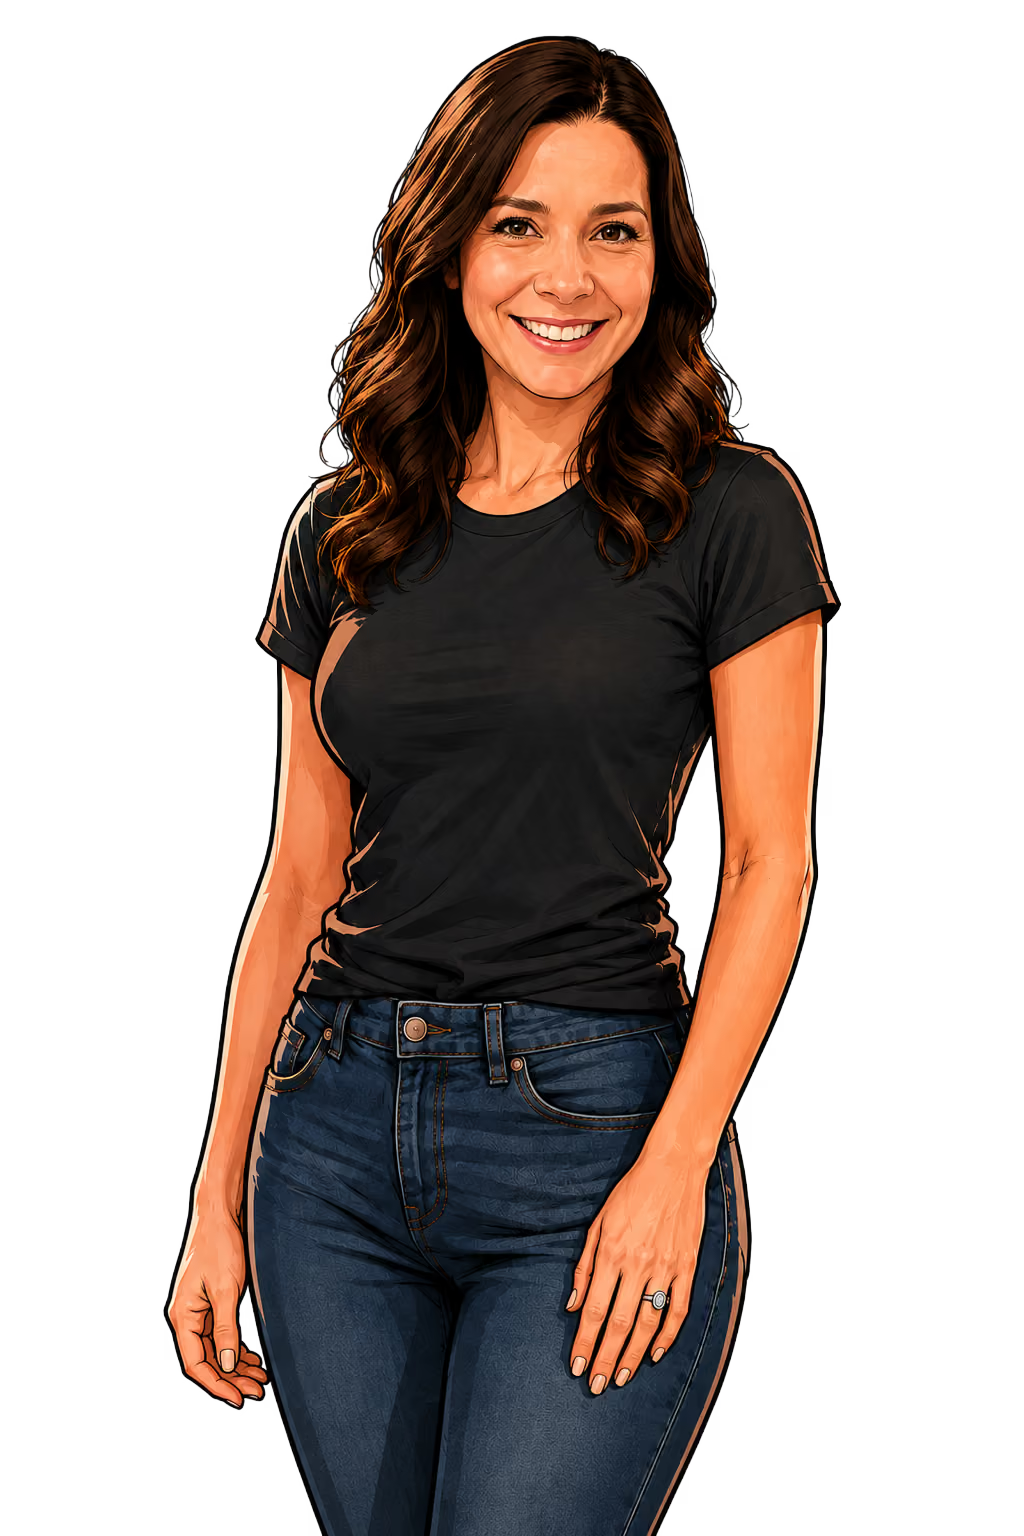
Vanessa Westfall
Vanessa drives operational excellence across STACKTITAN, aligning people, processes, and technology to support growth, service delivery, and client success. She specializes in translating strategy into execution within complex, security-first environments.
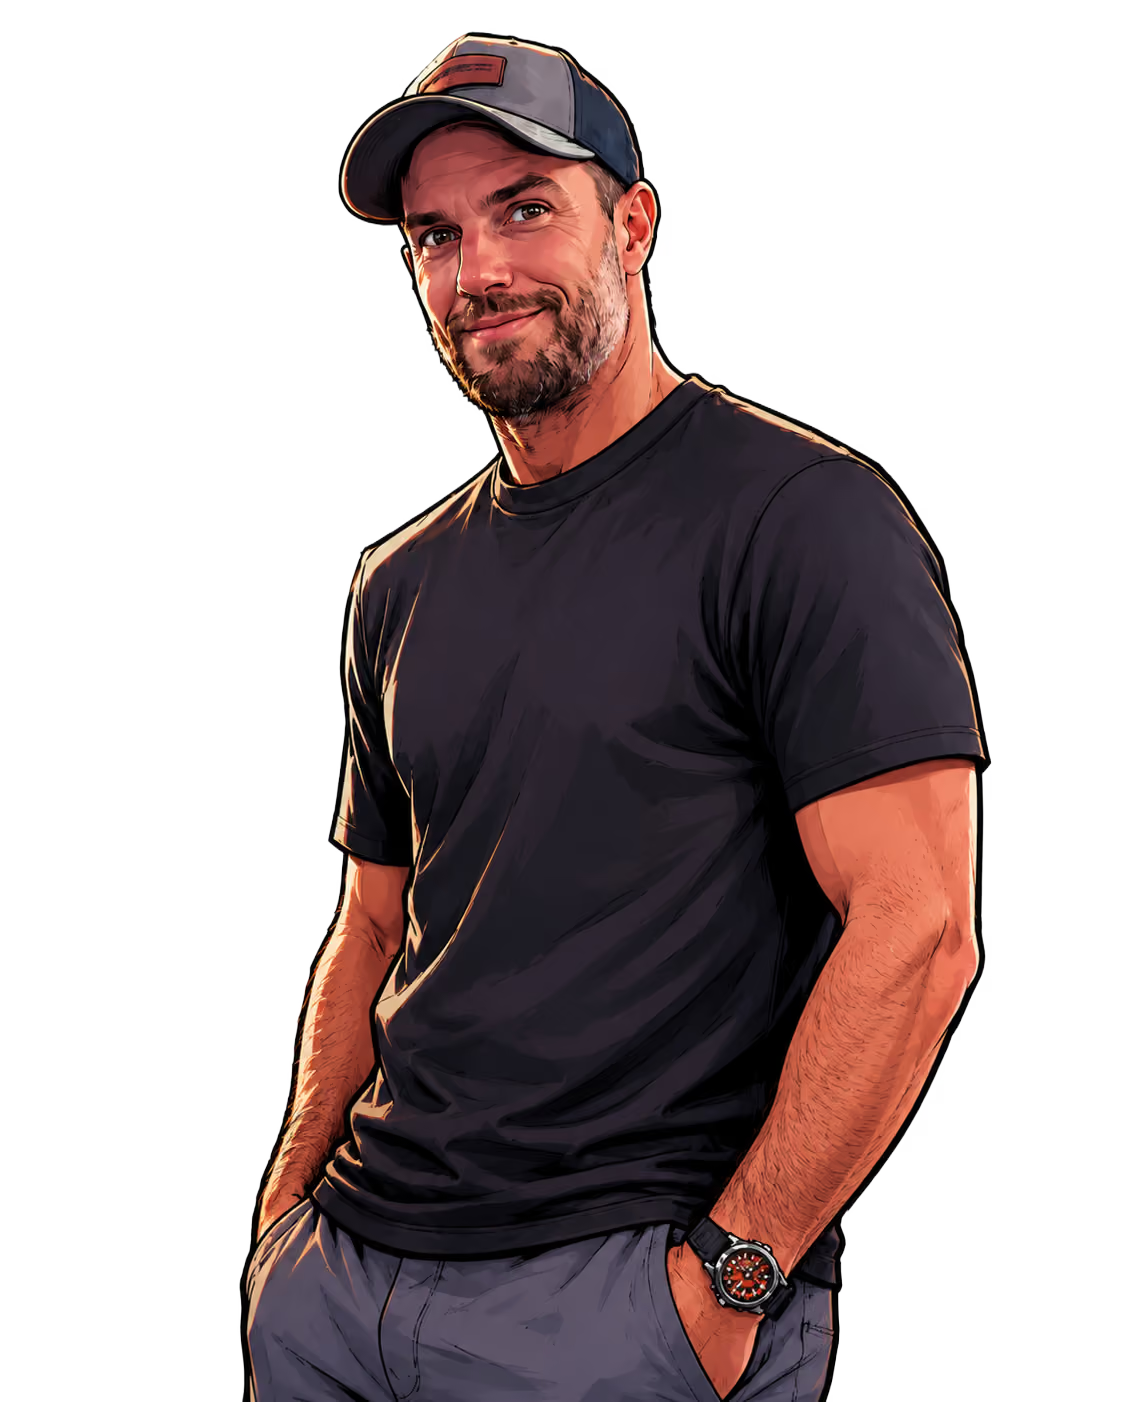
Jason Doelger
Offensive security specialist focused on penetration testing, adversarial simulation, social engineering, and physical security assessments. Helps organizations understand how attackers identify and exploit weaknesses across complex environments.
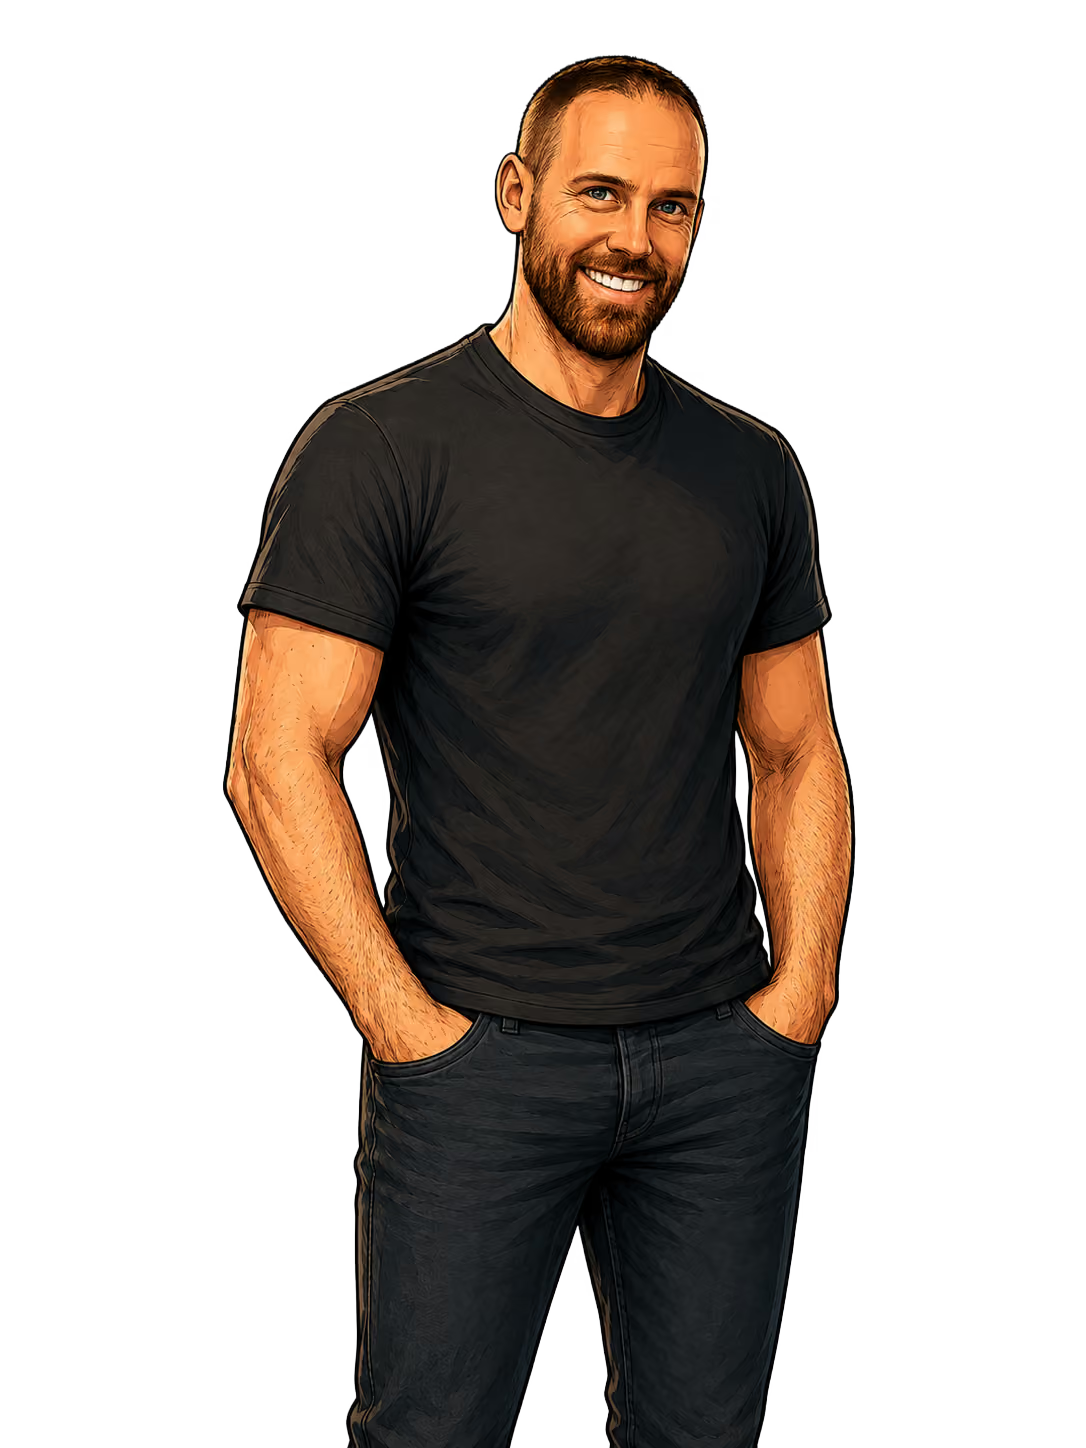
Matt Fisher
U.S. Army veteran with a background in military intelligence, digital forensics, and technical exploitation. Specializes in adversarial simulation, penetration testing, social engineering, and endpoint security assessments.
OUR PLATFORMS
Cerebral™
Cerebral™ is STACKTITAN's proprietary Intelligent Assessment Engine designed to bring together human expertise, targeted automation, tool orchestration, evidence management, cloud integrations, remote assessment capabilities, and continuous testing workflows.
The platform enhances offensive security engagements by improving consistency, increasing visibility, streamlining evidence collection, and helping organizations better understand risk across complex environments.
Rather than replacing human expertise, Cerebral™ enables STACKTITAN consultants to spend more time validating risk, uncovering attack paths, and delivering meaningful security outcomes.
Cloudhawk™
Cloudhawk™ extends STACKTITAN's offensive security methodology into cloud environments by continuously evaluating cloud assets, identities, services, configurations, permissions, and exposure pathways.
Integrated directly into the Cerebral™ ecosystem, Cloudhawk™ helps organizations identify cloud risk faster, validate controls more effectively, and understand how cloud weaknesses contribute to broader attack paths across the enterprise.
Whether operating in Azure, AWS, Microsoft 365, hybrid, or multi-cloud environments, Cloudhawk™ provides visibility into the risks that matter most.
Canopy™
Canopy™ extends the STACKTITAN model into continuous exposure management.
As a Cerebral™-powered service, Canopy™ brings together attack surface visibility, exposure validation, and human-led testing into a coordinated program for reducing risk exposure and increasing attack resiliency.
For customers, Canopy™ helps move security from periodic visibility to continuous understanding, showing what is exposed, what matters, and where action should be focused next.
Rather than relying on periodic assessments, Canopy™ helps organizations stay ahead of emerging threats by continuously reducing risk, improving attack resilience, and giving security teams the insight they need to make faster, more informed decisions.
Our values
Our values aren't slogans. They're operating principles.
They guide how we engage clients, how we make decisions, how we challenge assumptions, and how we measure success. Whether we're conducting a penetration test, building a platform, writing a proposal, or supporting a client, every member of STACKTITAN is accountable to the same standard.

Outcome over optics
We improve security, not complete engagements.
Success isn't measured by the number of findings, the size of a report, or the hours spent on a project. It's measured by whether our work helps clients reduce risk, make better decisions, and strengthen resilience.

No comforting fictions
Truth over comfort.
Our value comes from our willingness to say what others won't. If a risk is more severe than expected, a process is broken, or a strategy isn't working, we'll say so. Honest security advice is often uncomfortable, but it's always more valuable than false confidence.

Signal over noise
Volume isn't value.
Security teams are overwhelmed with alerts, dashboards, reports, and data. Our job is not to create more noise. Our job is to identify what matters, explain why it matters, and help clients focus on the actions that will have the greatest impact.

Stay dangerous
Stay curious. Stay current. Stay hard to compete with.
Attackers evolve constantly. So do we. We invest in research, experimentation, training, and continuous learning to ensure our methodologies, tools, and thinking remain ahead of the threats our clients face.

Hold the line
Craft separates us.
The Titan Standard applies to everything we produce—from a penetration testing report to a client email. We don't lower the bar because we're busy, tired, or under pressure. We deliver work we're proud to put our name on, every time.
STACKTITAN technical DNA
The best offensive security teams are built from diverse disciplines.
Security challenges rarely fit neatly into a single category, which is why STACKTITAN combines expertise from multiple technical backgrounds to better understand how modern attacks unfold.

Hackers
Real-world adversarial thinking uncovers vulnerabilities before malicious actors can exploit them.

Developers
Deep software engineering knowledge enables vulnerabilities to be identified closer to their source.

Researchers
Continuous research into emerging technologies and attack techniques keeps assessments aligned with the evolving threat landscape.

Creatives
Offensive security often requires unconventional thinking. Creative problem solving helps uncover attack paths that traditional assessments may overlook.

Architects
Architecture expertise provides insight into how applications, cloud platforms, networks, identities, and infrastructure combine to create organizational risk.

Educators
Knowledge sharing and collaboration help organizations build stronger internal security capabilities and long-term resilience.
Trusted by
Trusted by organizations where security is critical, STACKTITAN partners with enterprises across highly regulated and complex industries to validate risk, strengthen resilience, and protect the systems that matter most. From global brands to innovative technology providers, every engagement is focused on delivering measurable security outcomes.